
The Future of Crypto Trading: A Deep Dive into Technical Analysis APIs

A crypto technical analysis API is a programmatic interface that delivers real-time and historical market data alongside pre-calculated technical indicators – moving averages, RSI, MACD, Bollinger Bands – directly into trading applications. Rather than building indicator engines from scratch, developers and traders connect to these APIs to power dashboards, automated bots, and backtesting systems. As of Q1 2026, algorithmic systems account for an estimated 70–80% of global crypto trading volume, making API access a foundational layer of modern digital asset markets. What Is Technical Analysis in Crypto Trading? Technical analysis is the practice of studying historical price movements, trading volume, and market structure to identify patterns that suggest where prices may move next. It does not evaluate a project’s fundamentals or technology – it focuses entirely on what the market has done and uses that record to form probabilistic expectations about what it might do next. For crypto traders specifically, technical analysis addresses a real problem: most digital assets lack the financial statements, revenue histories, and analyst coverage that make fundamental analysis tractable for traditional equities. Price charts and volume data are available for every token, 24 hours a day, 365 days a year. That availability makes technical analysis a primary toolkit for crypto market participants. The three most widely used technical indicators across crypto platforms are: How Does a Crypto Technical Analysis API Work? An API (Application Programming Interface) is a communication bridge between two software systems. A crypto technical analysis API sits between raw exchange data and your application, handling the heavy lifting of data collection, normalization, and indicator calculation. The workflow typically looks like this: This approach saves teams weeks or months of engineering time. Computing a 200-period EMA across tick-level data from 400 exchanges is a significant infrastructure problem. APIs like TAAPI.IO, CoinAPI, and CryptoCompare solve it at the data layer so developers can focus on their actual product logic. For teams that want to handle indicator math themselves, open-source libraries like CCXT connect to more than 100 exchanges in Python, JavaScript, and Go – a useful alternative to commercial REST providers. Why Are Technical Analysis APIs Becoming Essential in 2026? The scale of algorithmic crypto trading has made programmatic market data access a practical necessity rather than a convenience. In Q1 2026, the AI crypto trading bot market was valued at $3.28 billion, with projections pointing to $12 billion by 2035 at a 13.9% CAGR. The broader algorithmic trading sector reached $18.73 billion in 2026. Platforms like Pionex now serve 5 million global users processing more than $60 billion in monthly trading volume, nearly all of it bot-driven. A newer development as of 2026 is API compatibility with the Model Context Protocol (MCP), which lets AI agents – not just traditional bots – pull live market data and indicators directly into reasoning pipelines. CoinAPI explicitly supports MCP, positioning crypto technical analysis data as a direct input to large language model-based trading agents. This signals a shift from API-as-tool to API-as-AI-collaborator. Three specific pressures drive API adoption regardless of whether the consuming system is a classic bot or an AI agent: Also Read: Top Crypto Technical Analysis Strategies What Are the Most Widely Used Crypto Technical Analysis APIs? API Provider Key Strength Indicators / Features Best For TAAPI.IO 200+ indicators calculated in real-time RSI, MACD, EMA, Bollinger, ATR, and more Trading bot builders CoinGecko API Free tier; 14,000+ assets tracked Price, volume, market cap, historical charts, DeFi/NFT data Developers and researchers CoinMarketCap API Largest market data breadth Real-time prices, global metrics, OHLCV Portfolio trackers and dashboards CoinAPI.io 400+ exchanges via one endpoint; MCP-compatible Tick-by-tick data, full order-book depth, AI agent support Institutional and HFT applications CryptoCompare 40,000+ API calls per second capacity Social data, blockchain data, pricing Real-time dashboards at high frequency Binance API Direct exchange access; lowest latency Live orderbook, klines, account management Binance-native trading bots Twelve Data Crypto + stocks + forex in one API Technical indicators, time series, WebSocket Multi-asset portfolio applications CCXT (open-source) 100+ exchanges; Python/JS/Go support; free OHLCV, order books, trade history, account management Custom bot builders with coding skills Bitquery On-chain DEX data via GraphQL DeFi trading, smart money flows, cross-chain DeFi analytics and on-chain analysis What Can You Build With a Crypto Technical Analysis API? How Do Automated Trading Bots Use These APIs? A trading bot is a program that monitors market conditions and executes trades based on predefined rules, with no human input required once it’s running. The bot queries the API at regular intervals (every minute, every tick), evaluates whether indicator thresholds have been crossed, and sends buy or sell orders to an exchange via a separate trading API. A practical example: a bot queries TAAPI.IO every 15 minutes for Bitcoin’s RSI on the 4-hour chart. When RSI drops below 30, the bot places a buy order on Binance. When RSI rises above 65, it sells. The strategy logic is simple; the API handles all indicator computation. BingX reported over $670 million in Futures Grid bot allocations in 2026, with more than 160,000 active grid bot users on that platform alone. The appetite for bot-accessible market data is not slowing down. How Do Backtesting Platforms Use Historical API Data? Backtesting means running a trading strategy against historical price data to see how it would have performed. APIs that provide years of OHLCV data across multiple timeframes make this possible at scale. Traders test indicator combinations to see, for example, whether a 9/21 EMA crossover outperforms a 50/200 crossover on Ethereum’s 1-hour chart, before risking real capital. Good backtesting requires clean, gap-free historical data. This is one area where paid API tiers consistently outperform free alternatives: institutional-grade providers normalize data across exchange restarts, market halts, and token splits in ways that raw exchange APIs often do not. Also Read: 8 Leading Indicators for Crypto Predictions What Else Can Developers Build? How Do You Choose the Right API for Your Use Case? Not all crypto APIs are equally suited to every application. The key variables to evaluate are:
South Korea Seeks to Delay Crypto Tax Until 2029
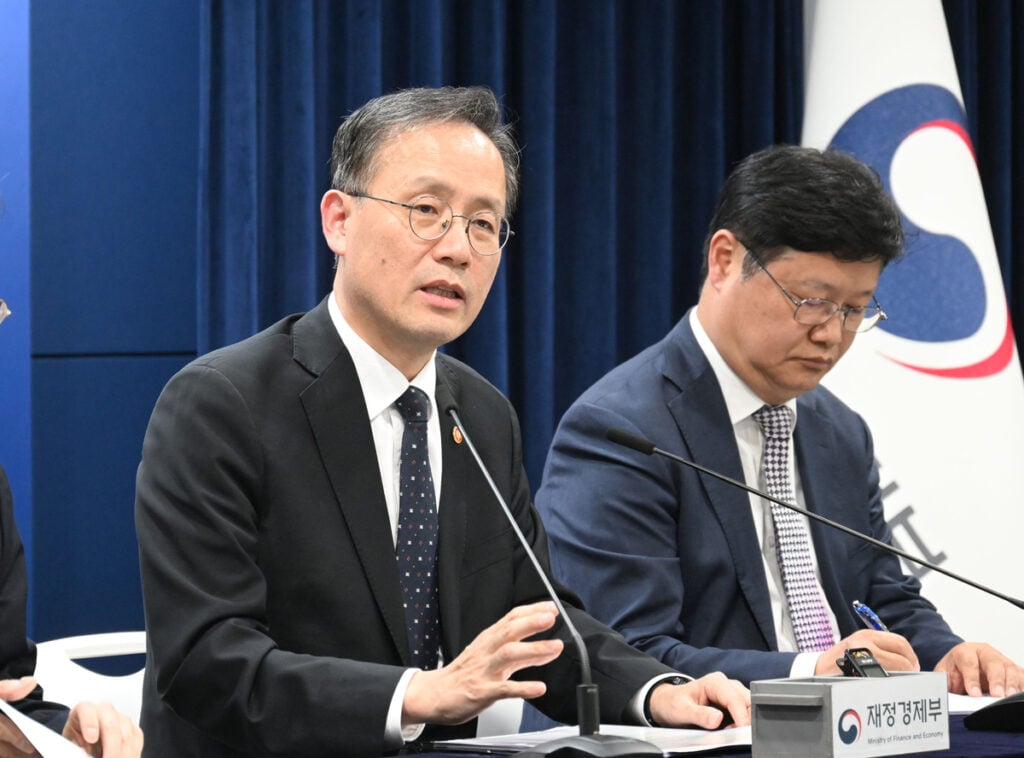
South Korea plans to seek another two-year delay to its cryptocurrency gains tax, moving the intended start from January 2027 to 2029. Finance Minister Lee Hyoung-il announced the proposal on November 5, citing gaps in overseas trading information and unfinished tax rules. The government will work with the National Assembly on the change. For traders, that distinction matters: the announcement sets out the government’s position, while the revised implementation date still requires legislative action. Key Takeaways Why the Government Wants More Time According to Yonhap’s report of the announcement, officials linked the proposed delay to the expected start of crypto transaction information exchanges with the United States in 2029. They warned that introducing the levy earlier could disadvantage South Korea’s domestic market. The issue is enforcement across trading venues. If authorities can obtain reliable records from domestic exchanges but have difficulty checking overseas activity, investors using different platforms may face uneven scrutiny. The government also wants to prepare for changes under broader digital asset legislation. That work concerns how assets, service providers and transactions fit into the regulatory framework, alongside the practical systems needed to calculate and report income. What the Planned Tax Covers The scheme awaiting implementation would apply a 22% rate, including local income tax, to annual cryptocurrency gains exceeding a 2.5 million won allowance. The proposal concerns postponing that income tax, rather than abolishing the principle of taxing crypto gains. If lawmakers approve the latest postponement, it would be the fourth delay since the tax was established for a planned 2022 introduction. The repeated changes make the legislative status particularly important when reading headlines that describe 2029 as a settled start date. This tax timetable is separate from exchange security obligations. South Korea’s latest exchange security review addresses wallet controls and incident readiness, which remain relevant regardless of when income taxation begins. Three-Year Loss Carryforward Proposed The government also wants investors to carry losses forward for up to three years and deduct them against future gains. That would recognise that a profitable year can follow a loss-making one in a volatile market. The proposed period describes how long an eligible loss could remain available for deduction. It does not mean the entire loss carryforward system would operate for only three years. Electronic Times’ briefing coverage says losses realised before taxation begins would not qualify under the proposed arrangement. Investors should therefore avoid assuming that every historical trading loss will become deductible when the system launches. What Happens Next A public-private working group will develop improvements to the tax system, with discussions planned through the first half of 2027. The government expects to submit related legislative amendments during the National Assembly’s regular session that year and announce detailed taxation standards in the first half of 2028. Areas requiring further work include lending, stablecoins and perpetual futures. Our guide to different stablecoin types provides background on why products grouped under one label can have different structures and uses. Traders can preserve exchange statements, acquisition costs, fees and wallet transfer records while the rules develop. Missing records can make later reconciliation harder, particularly when assets move between platforms. Sound wallet security practices also help protect access to assets during that preparation period. Conclusion South Korea’s government is seeking more preparation time for crypto taxation, alongside changes to loss deductions and reporting standards. The next decisive step is parliamentary action. Until the amendments and detailed rules are final, investors should follow official updates and keep complete transaction records.
South Korea Urges Crypto Exchanges to Tighten Security After Binance Hack
South Korea’s Financial Services Commission has urged domestic crypto exchanges to strengthen security following the Binance hack. An emergency meeting on November 2 reviewed wallet controls and incident readiness, followed by a broader financial-sector cyber defence announcement on November 5. The response goes beyond storing more assets offline. Authorities are examining the systems, staff permissions and external connections that can give attackers a route into financial infrastructure. Key Takeaways What the Exchange Review Covered In its November 2 announcement, the FSC said it met with the Financial Supervisory Service, Financial Security Institute, DAXA and major virtual asset businesses. The meeting assessed the Binance incident’s domestic implications and operators’ response systems. The regulator focused on access to computer systems, withdrawal approval and signing arrangements, and management of administrator privileges. It urged exchanges to increase cold-wallet holdings, monitor deposits and withdrawals continuously, secure more response personnel and share abnormal-access alerts quickly. Those priorities address several points in a potential attack. Keeping keys offline reduces one form of exposure, while permission controls determine who can reach the systems that authorise transactions. UEEx’s Binance incident report explains why employee devices and signing access came under scrutiny. Cold Storage Is an Existing Requirement The FSC’s guidance on the Virtual Asset User Protection Act sets a minimum cold-wallet holding level of 80% of users’ virtual assets by economic value. It also describes insurance or reserve requirements for incidents such as hacking and computer failure. The latest call to raise cold-wallet shares should therefore be distinguished from the existing baseline. The emergency meeting announcement did not establish a new universal percentage that every exchange must immediately meet. Storage ratios also need context. They describe the allocation of assets at a point in time, rather than proving that every device, approval process or withdrawal system is secure. Our wallet security guide explains how storage choices fit alongside other safeguards. Broader Inspections Announced on November 5 The FSC’s November 5 cyber defence update outlines inspections covering around 580 financial businesses. Checks include externally accessible systems, APIs, authentication, development environments and internal decision-making responsibilities. The regulator aims to complete inspections of registered external contact points by the end of November and internal-control examinations by year-end. It also plans guidelines requiring virtual asset service providers to report hacking incidents immediately to financial authorities, addressing a gap in the current reporting arrangements. A joint information-sharing system is scheduled for pilot operation in December, with wider adoption planned for the first quarter of 2027. These are implementation targets and proposed measures, rather than evidence that every component is already operating. What This Means for Exchange Users The review is a preventive response, not a statement that every participating exchange has suffered a breach. Customers should assess individual platform notices, supported services and withdrawal conditions instead of treating an industry-wide meeting as confirmation of losses at their provider. Connected trading tools also deserve attention. An exchange account can depend on external software for monitoring or order execution. Our SignalPlus API security update shows why reviewing those connections is a separate task from checking the exchange’s own infrastructure. Keep transaction records and use verified support channels when investigating a disruption. If an exchange changes service availability, check the stated reason and scope before assuming the same restrictions apply to every asset or network. Note when each announcement was issued, because a later operational update may replace an earlier warning or change the available services. Conclusion South Korea’s response combines immediate exchange checks with a wider cyber defence programme. The practical test will be implementation: stronger access controls, effective monitoring, clear reporting and verified remediation. Higher cold-storage shares can help, but they form only one part of protecting customer assets.
Polkadot Treasury Lost $1.38 Million After Security Fix Missed Production
Polkadot’s Treasury lost approximately $1.38 million in DOT value after a security fix failed to reach affected production runtimes, according to Parity’s November 2 incident review. The October 24–26 exploit distorted pricing in the DOT/dotUSD liquidity pool on Polkadot Asset Hub. The Treasury was the pool’s only liquidity provider. Parity says no users lost funds, while the incident exposed a gap between correcting vulnerable code and deploying that correction where it was needed. Key Takeaways How the Accounting Error Affected Prices Parity’s incident review says failed XCM instructions reduced recorded dotUSD issuance while account balances remained unchanged. That broke the expected relationship between total issuance and the sum of balances. The mismatch distorted the DOT/dotUSD pool’s pricing and created artificial exchange rates. The report says dotUSD remained backed, but the understated supply restricted redemption capacity pending correction. It has not established that the person exploiting the bug also profited from the subsequent arbitrage. For context on the network’s design, UEEx’s Polkadot explainer covers its cross-chain architecture. The incident concerned a specific execution and accounting failure, rather than evidence that all Polkadot wallets were compromised. The Fix That Missed Production As CryptoSlate reported from the review, Parity had received the bug report and merged a code fix in June. The fix missed a release cut-off and was absent from the runtimes affected in October. The initial medium-severity assessment had not accounted for interactions with dotUSD, which had not launched at that point. Parity later reclassified the issue as critical. The sequence illustrates why teams need to revisit earlier security assessments when new financial functionality depends on existing code. A merged patch and a deployed patch are different milestones. Reviewing a repository can show that developers addressed a bug, but confirming protection requires checking the version actually operating on-chain. A useful release check follows each security correction into the versions that need it, records which deployments remain exposed and verifies completion after the upgrade. That process becomes more important when several release branches and governance steps sit between a developer’s change and production. Why the Relayer Halt Only Delayed the Attack Snowfork initially halted its own consensus relayers, interrupting the attack. Parity says the attacker later ran an independent relayer and resumed before the corrective runtime took effect. Snowbridge’s documentation describes relayers as permissionless off-chain software that carries messages between blockchains. Anyone can operate one, subject to the protocol’s on-chain requirements. Stopping one operator’s software therefore does not necessarily stop every possible message route. The review places the underlying bug in the XCM executor and says it could be reproduced without Snowbridge. That distinction matters when describing responsibility: the route used to deliver a message is separate from the component that processes it incorrectly. Our cross-chain interoperability guide explains the broader role of these connections. What the Corrective Upgrade Changed The executed supply-correction referendum describes recorded dotUSD supply as approximately 4.06 million below the amount that existed. Its correction recalculated supply from existing balances without changing anyone’s balance. The proposal also restored Snowbridge settings affected by the previous runtime upgrade. Correcting supply accounting and repairing bridge operation were distinct tasks, even though they were handled together in the subsequent upgrade. For readers following remediation, the important evidence is the completed on-chain change and the behaviour it restores. UEEx’s crypto hacks archive provides context on how disclosures, containment measures and final repairs can represent different stages of an incident. Conclusion The Polkadot incident shows why security work must extend from bug discovery through production verification. The treasury loss was real, while user balances remained unchanged. Future assessments should track the deployed fix, corrected accounting and release controls separately, rather than treating a code update alone as completed protection.
BitMart Confirms New Hack as Restructuring Continues
BitMart founder Sheldon Xia has confirmed a November 2 hack while the exchange continues restructuring. The incident adds a security problem to an already difficult period for customers seeking information about their assets and the platform’s proposed recovery arrangements. Xia described the amount involved as small without giving a figure. Blockchain researchers have published their own estimate and identified wallet activity potentially connecting the incident to the Mercado Bitcoin attack. Key Takeaways What the Founder Confirmed In a November 3 post reported by crypto.news, Xia said BitMart had been hacked the previous day and had acted to investigate and strengthen security. He said a preliminary investigation pointed to the group behind the Mercado Bitcoin incident. Xia also described the security team as severely understaffed following restructuring and difficulties retaining technical personnel. That is the founder’s account of the staffing situation, rather than an independently audited assessment of the exchange’s controls. The public disclosure does not establish how the attacker obtained access. It also leaves open which specific wallets were affected and how the new incident relates to customer claims under the restructuring. What Blockchain Researchers Found In its updated investigation, Bitquery counts approximately $424,000 taken from wallets it links to BitMart. The report describes activity on Base, Arbitrum and Optimism, with additional amounts on five smaller networks. Its attribution uses address labels and transaction history. Bitquery says the receiving address also handled funds from the Mercado Bitcoin attack, and that the earlier transfers began around 53 minutes before Mercado Bitcoin’s main outflows. That overlap supports investigating a possible connection. It does not establish a shared technical vulnerability, supplier or initial access method. The estimate should remain attributed to Bitquery rather than presented as BitMart’s confirmed financial loss. Our Mercado Bitcoin reopening report covers the separate recovery process at the Brazilian exchange. Similar wallet activity does not mean the two companies have the same service-restoration timetable. Restructuring Predates the New Hack BitMart’s November customer notice says it announced a wind-down in July and stopped trading in August. Formal cessation of platform operations is scheduled for January 31, 2027. The notice describes proposed recovery options intended for a court-sanctioned process. Its indicative timetable calls for adjustments following user feedback during November, with court applications targeted for December 2026 or January 2027. Those are proposed milestones, rather than proof that a court has approved distributions or that customers can withdraw immediately. The latest hack and the broader restructuring should therefore be tracked as related but distinct developments. What Customers Should Check The exchange explicitly warns users not to deposit further assets. It says deposit services are suspended, transfers may not be automatically credited and addresses may still appear on some pages. A visible address is not confirmation that deposits are supported. Keep records of balances, transaction references and communications about any recovery option. Check the date and status of each notice before treating a proposed timetable as final. If you receive instructions about a claim, compare them with the official notice before submitting information. A message mentioning your exchange account or an authentic-looking logo does not establish that its sender is authorised. UEEx’s crypto hacks archive provides wider context on incident disclosures and loss estimates. BitMart also warns that there is no paid service for expedited withdrawals and that it will not request passwords, authentication codes, private keys or recovery phrases. Our guide to protecting crypto from hackers covers precautions against impersonation and credential theft. Conclusion The new breach raises further questions about security during BitMart’s restructuring. Customers should distinguish confirmed company statements, researcher estimates and proposed recovery terms, while avoiding new deposits and unofficial withdrawal offers. Clear updates on the investigation and restructuring process remain the next important developments.
Nigeria’s CBN Sets ₦15 Billion Capital Requirement for Foreign-Currency Stablecoin Issuers
Nigeria’s Central Bank has set a ₦15 billion minimum paid-up capital requirement for foreign-currency stablecoin issuers under a framework that took effect on November 5. Naira-referenced issuers face a ₦10 billion threshold, while other covered virtual asset service providers must maintain at least ₦1 billion. The rules create a more demanding entry process for businesses serving Nigerian users. Beyond capital, operators face licensing, reserve, redemption and reporting obligations that affect how stablecoin services are offered. The IMF highlighted the stakes in a June analysis, describing stablecoins as a growing cross-border channel in Nigeria. It warned that widespread use of dollar-denominated tokens could weaken demand for the naira and complicate monetary policy. That context helps explain why the new rules address payment activity and foreign-exchange exposure alongside customer protection. Key Takeaways Two Stablecoin Classes, Different Capital Floors The CBN regulations classify naira-referenced stablecoins as Class 1 and foreign-currency-referenced tokens as Class 2. Section 15 requires issuers to maintain the respective capital minimums on entry and throughout their operations, with the bank able to demand more. Section 16 sets a ₦1 billion floor for other non-security virtual asset services. For a provider holding a Securities and Exchange Commission licence, the CBN requirement is additional to the capital required by the securities regulator. The same capital cannot satisfy both obligations. These are business requirements, rather than minimum balances that individual customers must hold to use a service. Our guide to stablecoin types explains the different designs behind tokens that aim to track a reference asset. Local Licensing and Separate Reserves As TheCable reports, foreign-currency stablecoins must be issued through a Nigerian-incorporated entity holding the relevant CBN licence. Offshore ownership or affiliation does not remove that local obligation. The framework also requires approval for covered foreign-currency tokens offered in Nigeria. A familiar international ticker should therefore not be treated as evidence of Nigerian regulatory approval. Capital serves a different purpose from the assets backing tokens. The rules require it to remain separate from reserves, customer funds and operational liquidity. A company cannot describe the same pool of money as both its capital cushion and its token backing. Algorithmic Tokens and Redemption Controls Punch’s reporting on the framework says prohibited designs include algorithmic stablecoins relying primarily on supply adjustments rather than adequate reserves, and fiat-referenced tokens backed mainly by other cryptocurrencies. It also reports reserve requirements covering outstanding obligations plus an additional buffer, alongside redemption at face value generally by the next business day after a valid request. Those safeguards address backing and access to money, rather than the token’s name alone. UEEx’s explanation of algorithmic stablecoin models provides context on why reserve-backed and supply-adjustment designs carry different risks. Software can support a token’s operation without making every digitally managed stablecoin an algorithmic one. What Existing Operators Must Do TheCable reports three transition milestones from commencement: registration within 30 days, supervisory reporting within 60 days and complete licence applications within 180 days. The reporting period can be brought forward by the CBN. Continued activity during the transition is limited to existing scale and remains subject to the bank’s conditions. Missing the application deadline requires operators to stop until the necessary licence or authorisation is obtained. For customers, the practical issue is the provider’s actual status and the service covered. Watch for verified compliance notices and changes to supported products. Licensing rules also sit alongside technical safeguards; our wallet security guide explains precautions that remain relevant when using digital assets. Conclusion Nigeria’s new framework makes stablecoin issuance a capital-intensive, locally accountable activity. The next developments to watch are operator registrations, token approvals and implementation notices. A capital threshold establishes an obligation for businesses; it does not itself confirm that an individual issuer or token has met every requirement.
Mercado Bitcoin Plans Phased Reopening From November 9 After Security Breach
Mercado Bitcoin plans to begin restoring website access on November 9 following the security incident that disrupted its platform on November 2. Customers will initially be able to view account information, while trading, transfers and withdrawals remain unavailable. The Brazilian exchange says it will replace affected assets using company funds. The reopening plan gives customers a date for checking their holdings, but it does not yet provide a timetable for moving those assets. Key Takeaways What the First Reopening Phase Includes Mercado Bitcoin’s November 4 update says customers will be able to consult balances, statements, holdings and investments through its website. Other functions will follow as individual modules complete final security checks. The company says it is independently testing environments and transaction flows across its integrated custody, deposit, trading and balance-management systems. That makes the return of account viewing a separate milestone from the restoration of transaction services. For customers planning a transfer, that distinction matters. Seeing a balance confirms what the account displays; it does not show that withdrawals are operational. Follow the announcement for the specific service you need rather than treating “reopening” as a return to normal activity. Customer Balances and Replacement Assets In its updated incident FAQ, Mercado Bitcoin says customer balance records remain intact. It distinguishes those records from the assets held in its wallets to back them, some of which were removed during the incident. The exchange plans to purchase replacement assets with its own resources. Its November 4 statement says the trading desk is preparing repurchases in domestic and international markets. That commitment should be tracked separately from efforts to recover the stolen funds. Blocked assets are another category. A freeze can restrict an attacker’s ability to move tokens without immediately returning them to the exchange. Mercado Bitcoin’s latest figure of more than $16 million blocked is therefore a containment update, not confirmation that the same amount has already been restored to customer access. Blockchain Researchers Raise Timeline Questions In a November 5 investigation, Bitquery estimated that $48.6 million left Mercado Bitcoin wallets across 11 blockchains, valued at transfer-time prices. It also identified 36,042 Ethereum customer deposit addresses swept during the attack. Bitquery says those sweeps continued for about four hours after the exchange publicly described the incident as contained. That finding raises questions about the containment timeline, but blockchain transfers alone do not establish precisely how the attacker first obtained access. The researcher’s estimate should remain attributed rather than presented as a final reconciled company loss. UEEx’s crypto hacks archive provides context on how incident accounts develop as investigators identify additional wallets and transactions. What Happens to Open Orders? The latest company FAQ says all limit orders open before the November 2 interruption will be cancelled. Reserved amounts will return to available balances without charge. Mercado Bitcoin says prices changed during the outage, and customers might otherwise have orders execute under very different conditions when markets resume. Once trading returns, review the current market before submitting replacement orders. Keep earlier statements and order references for comparison. An order submitted before the outage reflects an earlier price and decision. Reconsider its size, limit price and purpose when services return, instead of automatically recreating instructions that may no longer match your plans. Our wallet security guide also explains why access and custody require different safeguards. Mercado Bitcoin warns against messages promising to release balances or requesting credentials. Use its verified channels and avoid unsolicited recovery offers. UEEx’s guide to protecting crypto from hackers covers related account-safety precautions. Conclusion The November 9 plan restores visibility first. Customers should watch for separate confirmation of trading and withdrawal availability, alongside progress on asset replacement. The next meaningful checkpoint is secure access to transactions, beyond the ability to view an account balance.
SignalPlus Reports Losses Below $82,000 as Binance and Deribit Revoke API Keys
SignalPlus says a cyberattack caused losses below $82,000 and that it has begun reimbursing affected users. The disclosure adds detail to a security warning that prompted Binance and Deribit to revoke API keys connected to the crypto derivatives trading platform on November 5. For traders, the immediate disruption reaches beyond the reported losses. Removing an API connection interrupts the software used to monitor accounts or automate trading, making direct checks on the underlying exchange especially important. Key Takeaways What SignalPlus Disclosed According to crypto.news’s account of the company’s statement, SignalPlus detected suspicious activity early on November 4. It traced the intrusion to a compromised vendor contact’s Telegram account, which an attacker used to send an engineer a fake Microsoft Teams invitation. The company said the engineer’s computer was compromised and the attacker later used employee access to target its internal network. SignalPlus contained the intrusion, suspended services for review and coordinated the removal of exchange API connections. SignalPlus acknowledged that it had not made IP whitelisting mandatory. It said a small number of accounts without that protection were affected and that reimbursements had begun on a case-by-case basis. The figures and repayment progress remain the company’s account of the incident. Why Exchanges Removed the Keys In an official notice, Binance said it removed all SignalPlus-linked API keys immediately as a precaution. It said its own systems were unaffected and customer funds remained safe. Reuters separately reported that Deribit revoked connected keys and found no indication that its systems or data had been affected. These statements concern the exchanges’ infrastructure; they should be read alongside SignalPlus’s disclosure of losses involving its service. A broad revocation is a containment measure. It cuts off an integration without requiring each customer to determine individually whether a credential was exposed. It does not, by itself, prove that every linked account suffered unauthorised activity. Trading Permission Still Carries Risk API keys allow software to perform the actions an exchange account authorises. Binance’s developer documentation distinguishes trading permissions from permissions used to monitor account information. A connection used only for viewing data has a different role from one allowed to submit orders. That distinction matters even when withdrawals are disabled. Unwanted trades can change exposure, incur fees or disrupt a hedging strategy. Removing withdrawal access therefore does not make a trading-enabled connection risk-free. IP whitelisting adds a restriction on where a key can be used. It works alongside limited permissions and secure key handling, rather than replacing them. UEEx’s wallet security guide explains the wider need to protect devices, credentials and access. What Connected Traders Should Check Binance advised customers to sign in directly, inspect positions and open orders, and wait until SignalPlus confirms resolution before linking new keys. Check each exchange separately if your setup uses several venues. Also confirm which monitoring or automated tasks stopped when the connection was removed. Do not assume that disabling a key has closed an existing position or cancelled every order. Review the exchange’s own account records and keep references for any disputed activity. Keep an inventory of connected tools and the permissions each one needs. That record makes it easier to identify unused access and understand which parts of your trading workflow depend on a single provider. Use verified support channels for reimbursement questions. Our guide to protecting crypto from hackers covers precautions against impersonation, while the UEEx crypto hacks archive documents other incidents affecting connected services and custody systems. Conclusion The SignalPlus incident shows why third-party access needs its own security checks. Traders should verify account activity directly, track the company’s reimbursement updates and review permissions before restoring an integration. An exchange remaining operational does not remove the need to check the tools connected to it.
Binance Says Fake Job Interview Helped Attackers Reach Wallet Systems
A fake job interview helped attackers reach Binance’s wallet infrastructure before its October 29 security incident, according to the exchange’s initial findings published on November 3. Binance puts the affected assets at approximately $6.34 billion. The report shifts attention from the stolen tokens to the employee computers and permissions that supported the attack. Its findings remain preliminary, with independent review still planned. Key Takeaways How the Attack Reached Wallet Systems In its initial incident report, Binance describes a September recruitment approach that ended with an engineer downloading a malicious coding assignment. The attacker later used an internal AI tool to reach colleagues’ computers, obtained deployment credentials and launched the attack through a deployed container. Binance says the intruder accessed an internal wallet-signing service and initiated transfers outside the normal withdrawal process. It has rebuilt affected systems, replaced devices and disabled related credentials. The company says it will absorb the financial impact. These disclosures describe more than an individual clicking a suspicious link. The important question for exchanges is how far compromised employee access can reach before another control stops it. UEEx’s crypto hacks archive provides broader context on the different systems targeted across the industry. Why Pausing Withdrawals Was Not Enough Binance says malicious Ethereum authorisations allowed further movements after withdrawals were suspended. That exposes a difference between stopping a platform’s service and cancelling permissions recorded on a blockchain. The EIP-7702 specification allows an ordinary Ethereum account to delegate execution to code at another address. The feature supports functions such as transaction batching and sponsored fees, but its security depends on what the account authorises. A delegation can persist beyond the transaction that establishes it. Disabling an exchange interface does not itself change that blockchain state. Removing the delegation requires the appropriate on-chain authorisation; the specification includes a mechanism using the zero address to clear delegation code. This does not mean EIP-7702 gives strangers unrestricted access to any wallet. Valid authorisation is still required. The distinction matters when interpreting headlines: a feature used after attackers gain signing access is different from an unauthenticated break into Ethereum itself. What Exchange Security Teams Should Review In its analysis, security firm StepSecurity recommends treating unfamiliar recruitment repositories as untrusted code. Disposable environments should have no production credentials, work sign-in sessions or connections to sensitive files. A convincing recruiter or a legitimate hosting platform cannot establish that downloaded code is safe. StepSecurity also recommends mapping the identities, credentials and machines internal AI tools can reach. Teams should log who initiated an action and which identity actually performed it, restrict deployment access and test emergency revocation procedures before an incident. The firm notes that Binance has not named the internal AI tool or disclosed the precise mechanism used to reach other machines. Identifying a particular commercial product as the cause would therefore go beyond the published evidence. For readers assessing custody arrangements, those are useful questions to ask alongside wallet storage methods. Our guide to crypto wallet security practices explains why protecting keys, devices and account access requires several safeguards. What Users Can Do Personal account controls cannot repair an exchange’s internal infrastructure. They still matter: use a unique password, enable strong authentication and access support through verified channels. UEEx’s guide to protecting crypto from hackers covers practical precautions against malware and account compromise. During a developing incident, keep withdrawal availability separate from compensation claims and promises of recovery. Preserve transaction records, check the exact asset and network involved, and avoid sharing credentials with anyone offering to “unlock” funds. Conclusion Binance’s initial account connects a recruitment lure to production access and wallet signing. The wider security lesson is that controls must follow that entire path. Independent review will be important in assessing the findings and the changes made after the breach.
Crypto Demand and Supply Zones: The Smart Money Blueprint.
Show me where the orders are, and I will show you where the market is going. This old trading adage highlights the core truth of modern technical price action. If you want to stop chasing erratic market swings and start trading with intent, Getting yourself acquainted Demand and Supply Zones Analysis in Crypto is the ultimate key. In this article, you will learn how to locate institutional order blocks, distinguish fresh zones from exhausted ones, and avoid common liquidity traps. You will also review practical breakout and reversal setups alongside essential risk management rules designed to protect trading capital. Read also: Crypto Scams: The SHIELD Guide to Spotting and Avoiding Every Fraud Type. What Are Supply and Demand Zones in Crypto Trading? A demand zone is a price area where buying pressure previously outweighed selling pressure, causing price to rise sharply. When price returns to that area, buyers tend to re-enter, creating another upward move. A supply zone is the exact inverse: a price area where sellers overwhelmed buyers, pushing price lower. When price rallies back to that zone, sellers typically re-emerge. This concept builds on the foundational work of Richard Wyckoff (1873–1934), who codified supply and demand dynamics into a structured methodology for reading markets. Wyckoff’s accumulation phase corresponds directly to demand zone formation, while his distribution phase maps to supply zone formation. What separates zones from static trendlines is their width. A zone captures the full candle body that caused the strong move, giving traders a realistic entry band rather than a single price tick that is nearly impossible to hit with precision. How Do You Identify Demand and Supply Zones on a Chart? Rapid Price Action (Base Origin): Look for areas where price spent very little time before launching into a strong, decisive directional move. A fast departure leaving behind minimal candles signals that heavy institutional limit orders were stacked at that price level. Quality zones feature a sharp move away from the base, clean candle structures at the origin, and minimal price overlap inside the zone. Volume Validation: High trading volume during the initial breakout away from a price area confirms genuine institutional participation. Conversely, low-volume zones carry high failure rates because they typically represent temporary order imbalances rather than substantial resting liquidity. Support and Resistance Confluence (Polarity): Traditional support and resistance levels frequently sit directly inside supply and demand zones. When a major support level breaks, it often flips into a supply zone through a principle known as polarity, attracting heavy order volume on retests and triggering sharp reversals. Momentum Indicator Confluence: While price action dictates where a zone is drawn, secondary tools like the RSI, MACD, and Fibonacci retracement levels (such as the 0.618 or 0.786 ratios) help validate whether momentum aligns with a potential reaction at that boundary. Higher-Timeframe Context (Trendlines): Zones should never be read in isolation. A demand zone that forms along an established higher-timeframe uptrend line carries significantly more statistical weight than one isolated in choppy, directionless price action Which Technical Indicators Help Validate Zones? While price action dictates zone placement, secondary tools improve confirmation: How Do Trendlines Define Zone Context? Zones do not exist in isolation. A demand zone forming along an established uptrend line carries significantly more weight than one forming in choppy, directionless price action. Channels help traders verify whether a zone sits at a logical turning point within the broader market structure. What Types of Supply and Demand Zones Should Traders Know? Not all zones behave the same way, the table below compares the main zone types by their origin pattern and typical behavior on retest. Zone Type Origin Pattern Typical Signal Strength Rally-Base-Drop (Supply) Price rallies into a base, then drops sharply Bearish reversal on retest Strong – base shows trapped buyers Drop-Base-Rally (Demand) Price drops into a base, then rallies sharply Bullish reversal on retest Strong – base shows trapped sellers Rally-Base-Rally (Demand) Price rallies, consolidates briefly, continues up Continuation demand on pullback Moderate – trend continuation context Drop-Base-Drop (Supply) Price drops, consolidates briefly, continues lower Continuation supply on pullback Moderate – trend continuation context Flipped Level Former support broken, retested as resistance Bearish (or vice versa) Variable – depends on break strength and volume What Factors Affect Crypto Supply and Demand Zone Reliability? Cryptocurrency markets are shaped by unique forces that alter how well a zone holds on retest. What Are the Main Trading Strategies Using Supply and Demand Zones? Trend Reversal Strategy at a Zone The most common zone-based trade is entering at a zone boundary in anticipation of a price reversal. A trader identifies a fresh demand zone, waits for price to return to it, and looks for a confirming candlestick pattern (such as an engulfing candle or pin bar) before entering long. The stop-loss sits just below the zone’s lower boundary. The word “fresh” matters significantly. A zone tested multiple times weakens with each touch because the pool of limit orders waiting there is gradually consumed. First-touch trades at fresh zones carry the highest mathematical probability. Breakout Trading Using Zones When price breaks decisively through a supply zone with a strong candle close and elevated volume, traders enter long, targeting the next supply zone higher. The broken supply zone then becomes a demand zone, and traders look for a retest of that level before adding to the position. Range-Bound Trading Strategy When price oscillates repeatedly between a clear demand zone at the low and a supply zone at the high, range-trading becomes effective. Traders go long at demand and short at supply, with tight stops placed just outside each zone boundary. Risk Management Rules Read also: Beyond the Hype: Why Is Bitcoin So Expensive? Conclusion Anyone can look at a crypto chart after a rally and explain what happened. True consistency comes from knowing where the move originated before it even starts. In a 24/7 market flooded with retail emotion and algorithmic noise, structural demand and supply zones analysis in crypto remains your ultimate defense against false breakouts and
Supply Chain Tokenization: How Blockchain Tokens Are Transforming Global Trade

Supply chain tokenization converts physical goods, documents, certifications, and ownership rights into programmable digital tokens recorded on a blockchain – giving every authorized participant a single, tamper-proof view of where a product is, what condition it is in, and who is responsible for it. Unlike traditional tracking systems that rely on siloed spreadsheets and paper documents, tokenized supply chains update automatically at every handoff, from raw material sourcing through final delivery. As of 2026, the global blockchain supply chain market is valued at approximately $3.25 billion and is projected to reach $21.29 billion by 2029, growing at roughly 59.8% annually as industries move from pilots into full production deployments. What Is Supply Chain Tokenization? Supply chain tokenization replaces paper records and disconnected databases with digital tokens that live on a distributed ledger. A token can represent a physical product batch, a shipping document, a compliance certificate, a carbon credit, or a payment right. Once issued, the token follows the product through every stage of its journey – accumulating verified data at each step from the supplier to the end consumer. The system links blockchain with IoT sensors, smart contracts, and enterprise resource planning (ERP) software to create a unified data layer across previously disconnected supply chain partners. Because blockchain records cannot be altered retroactively, every participant works from the same authoritative source of truth rather than reconciling conflicting reports after the fact. How Does Supply Chain Tokenization Work? The process begins when a manufacturer or supplier issues a digital token linked to a specific product, batch, or document. The token receives a unique identifier loaded with attributes: production date, origin location, weight, quality grade, and certifications. From that point, the token travels with the goods. At each handoff – warehouse, shipping port, customs, distributor, retailer – participants scan the product and record the transaction on the blockchain. IoT sensors feed real-time data on temperature, humidity, and GPS location directly into those records. Smart contracts then check whether conditions are met – cold chain compliance, customs clearance, payment terms – and trigger automatic actions such as releasing payment or flagging a shipment for inspection. Also Read: Ethereum Virtual Machine (EVM): How It Works, Gas, and 2026 Updates What Technologies Make This Work at Scale? Several technologies work together to support supply chain tokenization in live deployments: What Types of Tokens Are Used in Supply Chains? Not all tokens serve the same purpose. The type chosen depends on what is being represented and how it will be transferred or traded: Token Type What It Represents Typical Use Case Utility tokens Access to platform services Paying for tracking, verification, or data access fees Stablecoins Currency-pegged value Cross-border supplier payments without FX volatility Security tokens Ownership stakes or financial interests Tokenized invoices, trade finance instruments NFTs (non-fungible tokens) Unique physical items or certificates Luxury goods authentication, pharmaceutical batches Data tokens Access to external information feeds Customs data, commodity pricing, weather conditions What Are the Real Benefits of Tokenizing Supply Chains? The case for tokenization extends beyond tracking. It restructures how trust, payment, and data-sharing work across multi-party networks where no single participant can verify the others. How Does It Improve Transparency? All authorized participants – suppliers, logistics providers, retailers, and regulators – access the same real-time data. There are no conflicting spreadsheets or delayed reports to reconcile. Research shows that approximately 52% of supply chain companies that adopted blockchain recorded measurable improvements in transparency and traceability. Walmart’s blockchain food traceability system – built with IBM Food Trust – reduced the time to trace a product from farm to shelf from 6 days and 18 hours down to 2.2 seconds. How Does Tokenization Reduce Administrative Costs? Blockchain can cut supply chain administrative costs by up to 90% by eliminating manual document processing, reconciliation errors, and intermediary fees. Smart contracts automate payments upon delivery confirmation, reducing bank processing delays for international trade from days to minutes. As of 2026, over 12,500 blockchain supply chain deployments are active globally – a figure that reflects the real cost savings companies are capturing. How Does It Fight Fraud and Counterfeiting? Counterfeit goods cost the global economy over $500 billion annually. Immutable blockchain records make it far harder to introduce fake products into authenticated supply chains. De Beers’ Tracr platform assigns each diamond a unique token containing its weight, cut, color, clarity, and country of origin – making conflict diamonds provably traceable. Louis Vuitton and Prada have joined the Aura Blockchain Consortium to authenticate luxury goods using similar on-chain records. How Does Supply Chain Tokenization Compare to Traditional Tracking? Feature Traditional Systems Tokenized Blockchain Systems Record storage Siloed databases per company Shared distributed ledger Data verification Manual audits and third parties Cryptographic proof, automated Fraud risk High – documents can be forged Low – immutable records Payment settlement Days via banks and intermediaries Minutes via smart contracts Traceability speed Days to weeks Seconds Cross-border coordination Fragmented, paper-heavy Unified digital system Setup cost Low initial, high ongoing High initial, lower ongoing What Are the Most Important Real-World Examples? Company/Platform Industry Implementation Outcome Walmart + IBM Food Trust Food retail Tokenized farm-to-shelf tracking for leafy greens and mangoes Trace time cut from 6+ days to 2.2 seconds De Beers Tracr Luxury goods NFT certificates for individual diamonds with full provenance data Verifiable ethical sourcing; counterfeit prevention Aura Blockchain Consortium Luxury goods Louis Vuitton, Prada, and others authenticate products on-chain Consumer-verifiable product authenticity at point of sale Nestlé + IBM Food Trust Food/beverage Coffee bean tokens tracking farms in Brazil and Rwanda Sustainability claims backed by verified, auditable data VeChain Multi-industry IoT-integrated platform for food, automotive, and luxury sectors Real-time product authentication at consumer level S&P Global + J.P. Morgan (2026) Carbon markets Pilot to tokenize carbon credits launched July 2026 Standardized, tradeable carbon credit records on-chain Which Platforms Support Supply Chain Tokenization? Several enterprise-grade platforms serve different industry needs. VeChain integrates IoT hardware directly with its blockchain, making it well-suited for physical goods tracking. OriginTrail uses a graph-based data structure that
The 10 Best Bitcoin ETFs to Buy Right Now (2026 Rankings)

A Bitcoin ETF (exchange-traded fund) is a regulated investment vehicle that tracks the price of Bitcoin and trades on traditional stock exchanges, letting investors gain exposure to Bitcoin’s price movements without ever touching a crypto wallet. Since the SEC approved the first batch of spot Bitcoin ETFs in January 2024, billions of dollars poured into these products at a record pace, making them the fastest-growing new ETF category in market history. As of Q1 2026, iShares Bitcoin Trust (IBIT) alone holds over $67 billion in assets, and the combined spot Bitcoin ETF market has surpassed $120 billion in total AUM. Why Did Bitcoin ETFs Become a Major Investment Category? For years, the most practical way for institutional and retail investors to access Bitcoin through a standard brokerage account was the Grayscale Bitcoin Trust (GBTC), which launched in 2013 but traded at persistent premiums or discounts to Bitcoin’s actual price. Futures-based ETFs arrived in October 2021 when ProShares launched BITO, the first U.S. Bitcoin ETF, but futures products carry roll costs that erode returns over time. The real turning point came on January 10, 2024, when the SEC approved 11 spot Bitcoin ETFs simultaneously. These products hold actual Bitcoin in custody rather than futures contracts, giving investors direct price exposure without the tracking error that futures carry. The approval marked a historic shift in how regulators view Bitcoin as an investable asset, and the market responded immediately: IBIT gathered more assets in its first year than any ETF in history, according to CryptoSlate’s first-anniversary analysis. What Types of Bitcoin ETFs Are Available to Investors? Two main structures are currently available in the U.S. market: Spot Bitcoin ETFs hold actual Bitcoin as their underlying asset. The fund buys and custodies real Bitcoin, so the share price tracks Bitcoin’s market price very closely. These launched in January 2024 and quickly captured the majority of investor interest. Custodians like Coinbase Prime and Fidelity Digital Assets secure the underlying Bitcoin on behalf of shareholders. Futures-based Bitcoin ETFs do not hold Bitcoin directly. They hold Bitcoin futures contracts traded on the Chicago Mercantile Exchange (CME). Because futures contracts expire and must be rolled into the next contract month, these funds accumulate roll costs over time, particularly in contango markets where futures trade at a premium to spot. BITO is the largest example of this structure. As of 2026, futures ETFs have largely been displaced by spot products for long-term investors, though they remain relevant for short-term tactical trades in accounts that restrict spot commodity ETFs. What Criteria Should You Use When Evaluating Bitcoin ETFs? Not all Bitcoin ETFs are equally suited to every investor. Four criteria matter most: Recommended reading: Bitcoin Technical Analysis: A Comprehensive Guide What Are the 10 Best Bitcoin ETFs to Consider in 2026? How Does iShares Bitcoin Trust (IBIT) Compare to the Competition? BlackRock’s iShares Bitcoin Trust (IBIT) is the clear market leader. As of Q1 2026, it holds over $67 billion in AUM, making it not only the largest Bitcoin ETF but one of the largest ETFs of any kind launched in recent memory. IBIT charges a 0.25% expense ratio and uses Coinbase Prime for custody. Its bid-ask spread of 0.02% and daily trading volumes that regularly exceed hundreds of millions of dollars make it the most liquid Bitcoin ETF available. For most investors seeking straightforward Bitcoin exposure through a brokerage account, IBIT is the benchmark. Data from TheStreet’s Bitcoin ETF analysis confirms IBIT holds roughly 55% of all spot Bitcoin ETF assets globally. Is Fidelity Wise Origin Bitcoin Fund (FBTC) a Viable Alternative to IBIT? Fidelity Wise Origin Bitcoin Fund (FBTC) is the second-largest spot Bitcoin ETF by AUM, holding approximately $17 to $25 billion as of early 2026. What sets FBTC apart is that Fidelity custodies its own Bitcoin in-house through Fidelity Digital Assets, without relying on a third-party custodian. This vertical integration appeals to investors who value the Fidelity brand and want fewer counterparty links in the chain. The expense ratio sits at 0.25%, matching IBIT. For investors already using a Fidelity brokerage account, FBTC often provides the smoothest experience. According to Crypto Research Report’s comparative analysis, FBTC and IBIT track Bitcoin’s spot price with near-identical accuracy over time. What Makes ARK 21Shares Bitcoin ETF (ARKB) Worth Considering? ARK 21Shares Bitcoin ETF (ARKB), a joint product from Cathie Wood’s ARK Invest and 21Shares, held approximately $4.4 billion in AUM by early 2026. Its expense ratio of 0.21% is slightly below IBIT and FBTC, making it a cost-competitive option for fee-conscious investors. ARK’s brand recognition in thematic investing has attracted a loyal investor base, and the fund’s size ensures solid liquidity. ARKB custodies Bitcoin through Coinbase Prime. How Does Bitwise Bitcoin ETF (BITB) Position Itself in the Market? Bitwise Bitcoin ETF (BITB) is managed by Bitwise Asset Management, one of the longest-operating crypto asset managers in the U.S. The fund charges 0.20%, among the lower rates for spot ETFs, and Bitwise publishes proof-of-reserves data for its funds, a transparency practice that sets it apart from most issuers. As of 2026, BITB holds approximately $2 billion in AUM. It is a strong choice for investors who want a lower-cost spot ETF from a crypto-native issuer with an established compliance record. What About Invesco Galaxy Bitcoin ETF (BTCO)? Invesco Galaxy Bitcoin ETF (BTCO) is a collaboration between Invesco and Galaxy Digital, a firm with deep roots in institutional crypto markets. It charges 0.25% and uses Coinbase Prime for custody. BTCO’s distinguishing feature is its use of the Lukka Prime Reference Rate for pricing, which aggregates data from multiple exchanges to produce a more stable reference price. The fund’s AUM is smaller than top-tier products, but Invesco’s institutional distribution network provides strong backing for long-term viability. Also Read: Top 9 Crypto Tax Software Solutions in 2026 Is VanEck Bitcoin Trust (HODL) Still Relevant in 2026? VanEck Bitcoin Trust (HODL) charges a 0.20% expense ratio, among the lowest in the spot Bitcoin ETF category. VanEck has a long history in the ETF