Want to move your crypto from Ethereum to Solana or from Polygon to Arbitrum? You can’t do it directly because blockchains operate as separate networks that weren’t designed to communicate with one another. That’s where cross-chain bridges come in.
Cross-chain bridges connect these isolated ecosystems, making it possible to transfer tokens and data across different blockchains. They have become essential infrastructure for DeFi, processing enormous amounts of capital.
Over the past month alone, bridge protocols handled more than $14.3 billion in transfer volume, according to DefiLlama’s Bridge Volume Rankings. But convenience comes with risk.
Since 2021, cross-chain bridges have been among the crypto industry’s biggest security weak points, accounting for more than $4 billion in exploit-related losses.
In this guide, you’ll learn how cross-chain bridges work, why they’re frequent targets for hackers, the different bridge models available, and the key security checks to make before moving your assets.
Join UEEx
Experience the World’s Leading Digital Wealth Management Platform
No bridge is 100% safe. Even audited, well-funded bridges have been hacked for hundreds of millions of dollars. Never bridge more than you can afford to lose.
Native bridges beat third-party bridges for security. Official bridges like Arbitrum Bridge or Polygon PoS Bridge get more security investment than smaller, general-purpose alternatives.
Size and track record are trust signals. A bridge with steady TVL and volume for 6 months or more has usually earned that trust. Be extra careful with brand-new bridges holding under $50 million.
Audits help, but they don’t guarantee safety. Wormhole, Nomad, and Orbit Chain were all audited before they were hacked. Audits lower the odds of a bug but don’t erase them.
What Are Cross-Chain Bridges?
Cross-chain bridges are protocols that let you move tokens, and sometimes data, from one blockchain to another. They solve a basic problem: blockchains don’t share information on their own.
A bridge lets you take an asset like Bitcoin or ETH and use it on a different chain, usually through methods like lock-and-mint, burn-and-mint, or shared liquidity pools.
As a result, bridges are what make a “multi-chain” crypto world possible. However, they are also one of the most attacked pieces of software in the industry, with more than $4 billion stolen through bridge exploits between 2021 and 2026.
Blockchains Can’t Talk to Each Other on Their Own
Think about the early internet, before different computer networks could connect. Each one worked fine on its own, but they couldn’t share anything with each other.
Blockchains are similar. Ethereum, Solana, Polygon, and hundreds of other networks each run their own rules, their own tokens, and their own way of confirming transactions. None of them were built to recognize the others.
That creates real problems such as:
Liquidity gets stuck: Money sitting on one chain can’t easily help people on another chain.
Teams rebuild the same tools over and over: Every chain needs its own version of lending apps, exchanges, and wallets.
Users get boxed in: Say you hold Bitcoin but want to use it in an Ethereum lending app. Without a bridge, your only real option is selling on an exchange and buying something else. That’s slow, costs fees, and isn’t what you actually wanted to do.
Bridges exist to fix that isolation problem. A few concrete reasons they matter:
Reduce liquidity fragmentation: Bridges connect liquidity across blockchains, allowing users to access DeFi opportunities that would otherwise remain isolated.
Improve user experience: They enable smooth asset transfers between networks without relying on centralized exchanges.
Enable composability: Developers can combine the strengths of multiple blockchains, such as lower fees, faster transactions, or enhanced security, to build better applications.
Drive ecosystem growth: Emerging blockchains depend on bridges to attract users, liquidity, and developers, helping expand the broader multi-chain ecosystem.
Bridges vs. Layer 2s, Swaps, and Wrapped Tokens
People mix these up constantly, so here’s the short version:
Bridges vs. Layer 2s: Layer 2s like Arbitrum and Optimism make Ethereum itself faster and cheaper. Bridges connect separate networks, whether that’s two Layer 1s or an L1 and an L2. For a deeper look at how L2s work on their own, see our guide on Layer 2 Solutions Explained.
Bridges vs. atomic swaps: A swap trades one token for a different token. A bridge moves the same token (or a representation of it) from one chain to another.
Bridges vs. cross-chain DEXs: A decentralized exchange swaps tokens for other tokens. A bridge usually creates a wrapped version of your original asset on the new chain.
Bridges vs. wrapped tokens: Wrapped tokens are often the output of a bridge. When a bridge locks your ETH and mints wETH on another chain, that wETH is a wrapped token.
“Bridges are consistently the most exploited category of infrastructure in crypto, precisely because they concentrate large amounts of locked value behind a relatively small set of validation logic.” That’s the pattern security researchers keep flagging after each major bridge hack, and it applies squarely to lock-and-mint designs.
How Cross-Chain Bridges Work
Let’s explore how cross-chain bridges work
Three-Step Bridge Process
Most bridges follow the same basic three-step pattern, whether you’re moving stablecoins or ETH.
Step 1: You Send Your Tokens on the Source Chain
You send your tokens to the bridge’s smart contract on the chain you’re leaving. The contract either locks the tokens (holds them, taking them out of circulation) or burns them (destroys them permanently). Say you send 10 ETH to a bridge contract on Ethereum. That ETH now sits locked in the contract, waiting.
Step 2: The Bridge Verifies What Happened
This is the part where most hacks actually happen. Off-chain validators or relayers watch the source chain, confirm your transaction really happened, and sign off on it. Once enough of them agree, they send a verified message over to the destination chain.
If this verification step is weak, an attacker doesn’t need to touch your wallet at all. They just need to trick or bypass the validators.
Step 3: You Receive Your Tokens on the Destination Chain
The bridge contract on the new chain receives the verified message and either mints a wrapped version of your tokens or releases them from a liquidity pool. Your 10 ETH might show up as 10 wETH on Solana, sent straight to your wallet there.
Going back the other way works in reverse, which is called bridging back; your wrapped tokens get burned on the destination chain, a message gets sent back to the original chain, and your original tokens get unlocked.
The Three Things Every Bridge Needs to Work
These are the key components that make bridges work
1. Smart contracts
These are the self-running programs that lock, mint, burn, and unlock tokens. If there’s a bug here, it can be catastrophic, since these contracts often hold hundreds of millions of dollars.
2. Validators and relayers
These are the people or systems watching both chains and approving transfers. They can be a handful of trusted parties or a large, decentralized network. The 2022 Ronin hack happened because attackers only needed to compromise 5 of 9 validators to steal $624 million.
3. Oracles
These feed outside information into the bridge, like verifying that a transaction on another chain actually occurred. If an oracle can be fooled or manipulated, so can the bridge.
5 Types of Cross-Chain Bridges
Not all bridges work the same way. Here’s what’s actually happening under the hood of each type.
1. Lock-and-Mint Bridges
You lock your original tokens in a contract on the source chain. The bridge mints (the process of generating new digital assets or tokens and recording them on a blockchain) an equal amount of wrapped tokens on the destination chain. This is the most common design, used by roughly 6 out of every 10 bridges in the market.
Real example:
Wormhole: Wormhole connects more than 20 chains, including Ethereum, Solana, and BNB Chain, using a network of 19 independent validators called Guardians.
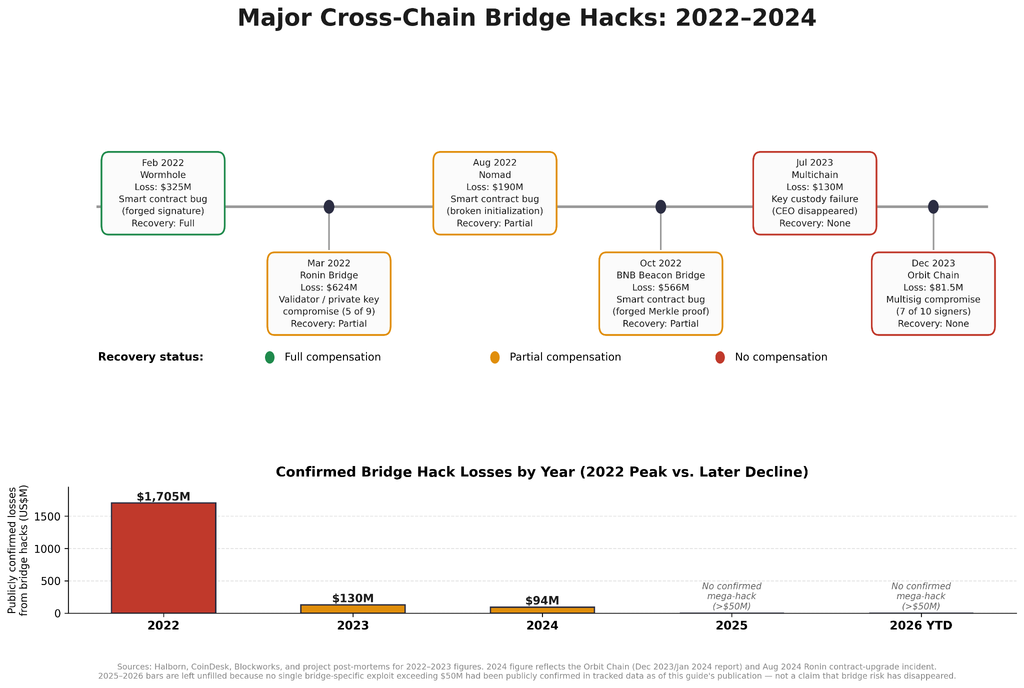
However, in February 2022, a bug in its signature verification let an attacker mint 120,000 wrapped ETH without ever locking any real collateral, draining $325 million. Jump Trading, Wormhole’s backer, covered the loss out of pocket so users didn’t lose funds.
Pros: works with almost any token, keeps total supply consistent across chains, flexible for connecting many networks.
Cons: wrapped tokens can be less liquid than the originals, a single contract bug can drain the whole bridge, and validator compromise is a real risk.
2. Burn-and-Mint Bridges
Here, your tokens get burned (destroyed) on the source chain, and new native tokens get minted on the destination chain. This only works if the token already exists natively on both chains, so it’s less common than lock-and-mint.
Real example:
Polygon PoS Bridge: Moving MATIC from Ethereum to Polygon uses lock-and-mint. Moving it back uses burn-and-mint, releasing tokens from Polygon’s supply. The Polygon PoS Bridge has kept a strong security track record, helped by continuous maintenance from the Polygon team, and typically settles transfers within 5 to 10 minutes.
Pros: no confusing wrapped tokens, cleaner mental model, usually simpler contracts.
Cons: only works for tokens that already exist on multiple chains, so it can’t move arbitrary tokens the way lock-and-mint can.
3. Liquidity Pool Bridges
Instead of minting or burning anything, these bridges keep pools of tokens sitting on both chains. You deposit into the source pool, and the bridge immediately pays you out from the destination pool. No waiting for new tokens to be created.
Real example
Synapse Protocol: Synapse supports more than 20 chains and started out focused on stablecoins before expanding to other assets. Liquidity providers earn fees for supplying the pools that make instant transfers possible. Because there’s no minting delay, transfers typically settle in 2 to 5 minutes, among the fastest of any bridge type.
Pros: Fastest transfers, true swaps rather than wrapped assets, better user experience when liquidity is deep.
Cons: Needs deep liquidity on both sides to work well, big trades can suffer slippage if a pool is thin, and liquidity providers carry their own risk of impermanent loss.
4. Optimistic Verification Bridges
These bridges assume transactions are honest by default. A transaction gets posted, and there’s a challenge window, often 1 to 7 days, during which “watchers” can flag fraud. If nobody flags it, the transfer finalizes.
Real example:
Nomad Bridge: Nomad used this design before its August 2022 exploit. A bug in how the contract was initialized meant anyone could act as a valid watcher, essentially skipping verification altogether. Attackers realized this and, in what became known as a “copy-paste” attack, more than 300 different wallet addresses joined in and drained $190 million, many of them just copying the first attacker’s transaction and swapping in their own address.
Pros: cheaper to run than full verification, can process high volume, faster settlement in most cases than fully verified systems.
Cons: the challenge period delays true finality, and the whole model depends on watchers actually doing their job. When that assumption breaks, so does the bridge.
5. Intent-Based Bridges
This is the newest approach. Instead of telling the bridge exactly how to move your funds, you just state what you want: “I want 1,000 USDC on Arbitrum.” A network of competing relayers bids to fulfill that request, usually fronting the capital themselves and getting repaid once the transfer settles.
Real example
Across Protocol: Across focuses on transfers between Ethereum Layer 2s and uses a request-for-quote system where relayers front the funds instantly, with settlement verified afterward. Because relayers compete for your business, fees on some routes run as low as a few basis points.
Pros: simplest user experience by far, often the cheapest option thanks to relayer competition, no wrapped tokens to manage.
Cons: still newer and less battle-tested than older bridge designs, and it depends on having enough relayers willing to front liquidity.
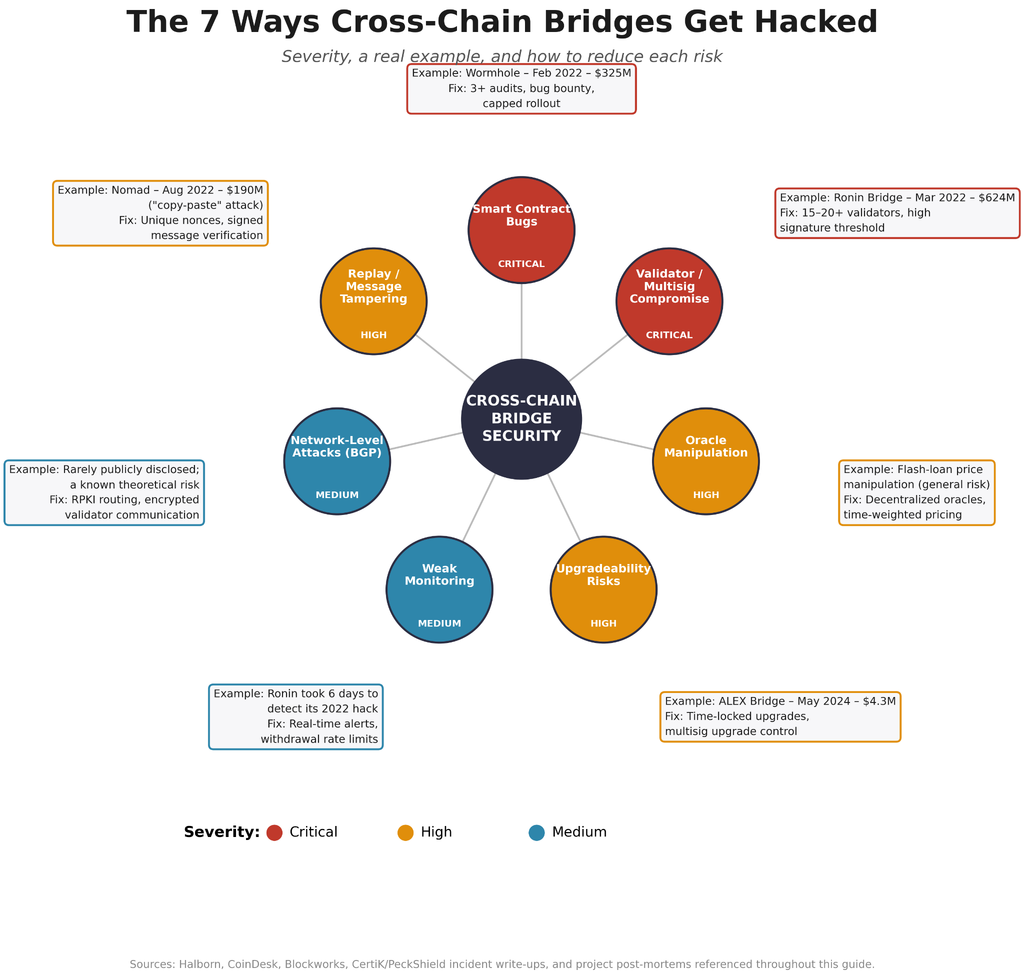
Bridge Security: 7 Ways Bridges Get Hacked
Below are the seven different ways cross-chain bridges get hacked
1. Smart Contract Bugs
Bridges lean heavily on smart contracts to lock, mint, burn, and unlock funds. A single coding mistake, even a small one, can be catastrophic, and once it’s live, it’s hard to patch quietly.
Wormhole (February 2022): A signature verification flaw let an attacker mint $325 million in wrapped ETH with no real backing.
Nomad (August 2022): A broken initialization check let anyone bypass verification, leading to a $190 million free-for-all.
BNB Chain’s Beacon Bridge (October 2022): A flaw in how the bridge verified proofs let an attacker forge 2 million BNB, worth about $566 million at the time.
How to reduce this risk: Look for multiple independent audits from firms like CertiK, Trail of Bits, or Halborn. Also check for an active bug bounty program and a history of gradual, capped rollouts rather than launching with unlimited deposits on day one. Chainlink’s research on cross-chain risk is a good place to see how these failure points get categorized in more technical detail.
2. Validator or Multisig Compromise
Many bridges rely on a small group of validators or a multisig wallet to approve transfers. If attackers control enough of that group, they can approve fraudulent withdrawals without touching a single smart contract bug.
Ronin Bridge (March 2022): attackers compromised 5 of 9 validator keys and drained 173,600 ETH and 25.5 million USDC, worth about $624 million. The U.S. FBI later attributed the attack to North Korea’s Lazarus Group.
Multichain (July 2023): the company’s CEO disappeared, and roughly $130 million was withdrawn without authorization across several chains.
Orbit Chain (December 31, 2023): attackers accessed 7 of 10 multisig signers, funded through Tornado Cash, and stole about $81.5 million in stablecoins, ETH, and wrapped Bitcoin.
How to reduce this risk: favor bridges with larger, more spread-out validator sets (15 to 20 or more), a high signature threshold to approve transfers, and validators run by genuinely different, unrelated organizations.
Security firm Halbornsummed up the root cause of the largest bridge hack in history plainly: the Ronin Network was, in practice, controlled by nine validators, four of them owned by the same company, and a fifth was reachable through a program that hadn’t been properly shut down.
3. Oracle Manipulation
Bridges often depend on oracles for pricing and cross-chain data. If that data can be manipulated, even briefly, an attacker can exploit the gap. Flash loans are a common tool for temporarily distorting prices just long enough to profit.
How to reduce this risk: decentralized oracle networks, time-weighted pricing that resists sudden spikes, and automatic circuit breakers for abnormal price swings all help.
4. Upgradeability Risks
Many bridge contracts are upgradeable, meaning the team can push code changes after launch. That flexibility is useful for fixing bugs, but it also means whoever controls the upgrade keys holds enormous power. If those keys are compromised, or if an upgrade itself introduces a new bug, the whole bridge is exposed.
How to reduce this risk: look for time-locked upgrades (which give users a warning window to exit), multisig control over upgrade permissions, and public review processes before changes go live.
5. Weak Monitoring and No Circuit Breakers
Without real-time monitoring, an exploit can drain a bridge long before anyone notices. As a result, speed matters here. A few minutes of delay in detection can mean the difference between losing thousands and losing hundreds of millions.
How to reduce this risk: bridges with automated anomaly detection, withdrawal rate limits, and a dedicated security team watching around the clock tend to catch and contain problems faster.
6. Network-Level Attacks (BGP Hijacking)
While most bridge security focuses on smart contracts, BGP (Border Gateway Protocol) attacks target the internet’s routing layer. By hijacking IP prefixes, attackers can reroute validator traffic, enabling man-in-the-middle attacks, service disruption, or transaction delays before data even reaches the bridge. As blockchain infrastructure grows, securing the network layer is just as important as securing on-chain code.
How to reduce the risk:
Deploy RPKI (Resource Public Key Infrastructure) to validate BGP route announcements.
Encrypt all validator-to-validator communications.
Use redundant network paths and failover infrastructure.
Include routing security reviews alongside smart contract audits.
Follow MANRS routing security best practices to strengthen network resilience.
7. Replay Attacks and Message Tampering
Replay attacks occur when attackers resend a previously valid cross-chain transaction or message, potentially triggering duplicate transfers or double-spending. Weak message validation can also allow forged or altered cross-chain messages to be executed. Modern bridge exploits often stem from poor nonce tracking and inadequate replay protection.
How to reduce risk:
Use unique, sequential nonces for every transaction to prevent message reuse.
Verify cryptographic signatures and bind them to the source and destination chain IDs.
Track processed message hashes and reject duplicate or out-of-order messages.
Enforce strict message format and payload validation before execution.
Add timestamp or expiration checks where appropriate to invalidate stale messages
Bridges aren’t isolated pieces of plumbing. They’re load-bearing walls for the rest of DeFi.
Most DeFi protocols depend on bridged assets to operate across chains. If a major bridge like Wormhole went down tomorrow, lending platforms, DEXs, and yield strategies on Solana, Avalanche, and Polygon that rely on bridged Ethereum assets would all feel it immediately.
That risk shows up in a few ways:
Direct exposure: if a bridge gets hacked, the wrapped assets it issued can become worthless overnight, and anyone holding them takes the loss directly.
Liquidity cascades: panic after an exploit often triggers mass unwrapping, which can drain liquidity pools that had nothing to do with the original hack.
Confidence contagion: one bridge hack tends to spook users away from other bridges too, even ones that were never at risk.
Bridge insurance exists through platforms like Nexus Mutual, but coverage remains thin relative to the total value moving through bridges, and premiums (often 2 to 5% annually) are steep enough that most users skip it entirely.
Bridges aren’t just a target; they’re also a getaway car.Chainalysis’s 2026 Crypto Crime Reportfound that North Korean hackers regularly move stolen crypto through cross-chain bridges as part of a structured laundering process, using them to fragment and obscure fund movement across blockchains before cashing out.
How to Choose a Safe Cross-Chain Bridge
Here’s a practical framework for evaluating any bridge before you use it.
1. Check the Audit History
Look for at least 3 independent audits from firms with real track records, like CertiK, Trail of Bits, Halborn, OpenZeppelin, or Quantstamp. Check whether critical findings were actually fixed, not just reported. See if there’s an active bug bounty program on a platform like Immunefi.
Red flags: no audits, audits over 18 months old with nothing since, or unresolved critical findings.
2. Look at Hack History and How the Team Responded
Has the bridge been hacked before? If so, what happened next matters almost as much as the hack itself. Wormhole’s backer covered $325 million in losses within days. Multichain’s CEO vanished, and users were never made whole. That difference tells you a lot about who you’re trusting with your funds.
3. Check TVL and Volume
Bigger, more consistent numbers usually mean more capital at risk, which usually means more security investment. You can check current bridge volume and total value locked directly on DefiLlama’s bridge dashboard or on L2Beat’s bridged TVL rankings.
Rough guide:
Steadier bet: $500 million or more in TVL, sustained for 6+ months
Moderate: $100 million to $500 million
Riskier: under $100 million, or live for less than 3 months
A sudden 50% drop in TVL over a short window is a warning sign worth investigating before you send anything.
4. Look at the Validator Setup
A bridge’s validator network is its first line of defense. The safest protocols rely on decentralized validators with high signature thresholds, making it difficult for a small group to approve fraudulent transactions.
For example, Wormhole uses 19 Guardian validators with a 13-of-19 quorum, while Chainlink CCIP secures cross-chain messaging through a decentralized network of independent node operators.
Signature threshold: Aim for 80%+ approval (e.g., 7/9 or 16/20).
Validator identity: Known, reputable organizations are preferable to anonymous operators.
Diversity: Validators should be spread across different companies, regions, and infrastructure providers to reduce concentration risk.
5. Compare Fees and Speed
Cross-chain bridge costs typically include source-chain gas fees, a bridge protocol fee (around 0.05%–0.5%), destination-chain gas fees, and, for liquidity-based bridges, slippage of roughly 0.1%–2%. Actual costs depend largely on network congestion.
Native optimistic rollup withdrawals (Arbitrum → Ethereum): about 7 days because of the mandatory fraud-proof challenge period.
6. Confirm It Supports Your Chains and Assets
Before choosing a crypto bridge, make sure it supports the blockchains and tokens you want to transfer. For broad cross-chain compatibility, Wormhole and Synapse connect dozens of networks, while Stargate uses LayerZero to support transfers across a large multichain ecosystem.
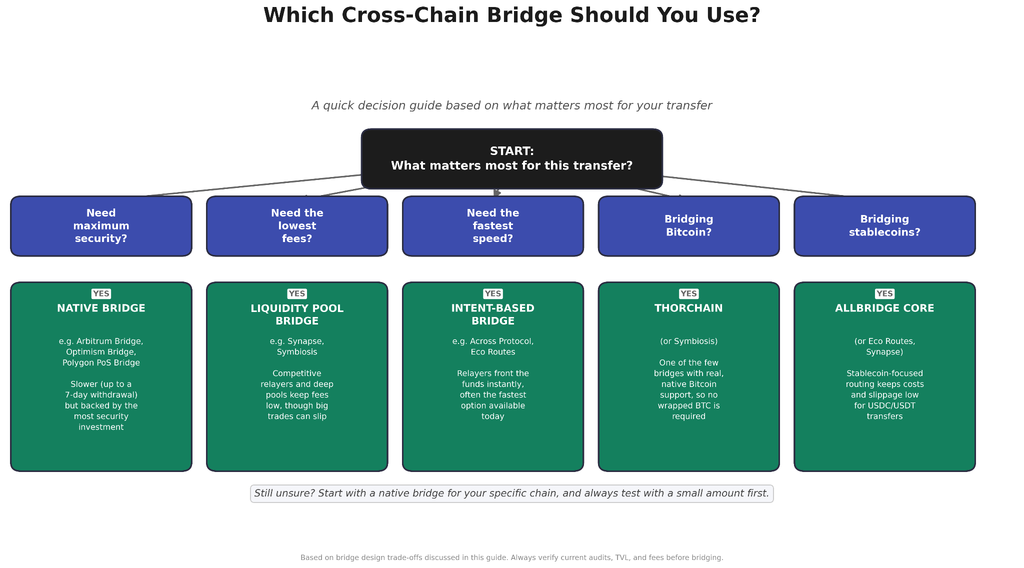
Multi-chain users: Wormhole, Synapse, and Stargate
Ethereum L2s: Native Arbitrum Bridge and Optimism Bridge
Stablecoins: Allbridge Core and Eco Routes
Bitcoin support: THORChain and Symbiosis
Always verify that your bridge supports the exact asset you want to move. Some only handle major tokens like ETH, USDC, USDT, and WBTC, while others support hundreds of assets.
7. User Experience & Tools
A reliable bridge should make cross-chain transfers simple, transparent, and secure. Look for a clean interface, real-time transaction tracking through a block explorer, clear error messages with recovery options, responsive Discord or Telegram support, and smooth compatibility with mobile wallets. Modern bridges also provide live progress updates to reduce uncertainty during transfers.
Before transferring large amounts, always:
Test with $10–$50 first to verify the bridge works as expected.
Track the transaction until it is confirmed on the destination chain.
Confirm the funds arrive in your destination wallet before proceeding.
Increase the transfer amount only after a successful test, minimizing the risk of costly errors.
Where Bridges Are Headed
Cross-chain bridging is evolving rapidly. Instead of simply moving tokens between blockchains, the next generation of bridges is focused on making transfers faster, safer, and almost invisible to the end user.
Intent-Based Bridging Is Becoming the Standard
One of the biggest shifts is the rise of intent-based bridging. Rather than manually selecting a bridge, route, and gas settings, users simply specify the outcome they want, for example, “Send 500 USDC from Ethereum to Base.”
A network of competing relayers or solvers then finds and executes the most efficient path. Protocols such as Across and Eco Routes are leading this transition, making cross-chain transfers significantly simpler for both retail users and developers.
Native USDC Is Replacing Wrapped Versions
Another major trend is the growing adoption of native USDC over bridged alternatives like USDC.e. Through Circle’s Cross-Chain Transfer Protocol (CCTP), USDC is burned on the source chain and freshly minted on the destination chain, eliminating many of the risks associated with wrapped assets. More bridge providers, including Across, are now routing transfers through CCTP to improve security and reduce user confusion.
Bridge Aggregators Are Doing the Heavy Lifting
Bridge aggregators are also transforming the user experience. Instead of comparing multiple protocols manually, platforms such as LI.FI, Socket, and Bungee automatically evaluate available routes and select the best option based on fees, speed, liquidity, and reliability.
This saves users time while helping them avoid unnecessary costs and inefficient transfers. LI.FI has even expanded into intent-based execution, reflecting the industry’s broader move toward automated cross-chain transactions.
Regulation Is Beginning to Catch Up
Regulators are also paying closer attention to cross-chain infrastructure. In Europe, the Markets in Crypto-Assets (MiCA) framework is now fully in force, meaning bridge operators that custody assets or issue wrapped tokens may face licensing, governance, and compliance obligations.
Meanwhile, U.S. regulators, including the SEC, CFTC, and FinCEN, continue evaluating how existing securities, commodities, and anti-money laundering rules apply to bridge services. While dedicated bridge legislation has yet to emerge, clearer compliance requirements are expected as cross-chain activity becomes more mainstream.
Join UEEx
Experience the World’s Leading Digital Wealth Management Platform
Cross-chain bridges aren’t going anywhere. With well over a thousand blockchains now running, they’re the only real way to keep crypto from splitting into a thousand disconnected corners. But that usefulness comes with risk that isn’t going away either.
The safest approach isn’t finding a “perfectly safe” bridge, because one doesn’t exist. It’s understanding how each bridge works, checking its track record before you trust it with your money, and never moving more than you’re prepared to lose. Treat every cross-chain bridge transaction with the same care you’d use handling cash, because in a very real sense, that’s exactly what you’re doing.
What is the difference between a cross-chain bridge and a Layer 2?
A Layer 2 makes an existing blockchain, usually Ethereum, faster and cheaper to use. A cross-chain bridge connects two separate blockchains so assets can move between them. You can think of an L2 as adding an express lane to an existing highway, while a bridge is a new road connecting two different highways entirely.
Can I lose money if a bridge gets hacked after I’ve already bridged my assets?
Yes, if the bridge that issued your wrapped tokens gets hacked, those tokens can lose their value even if you’re not the one being directly attacked, since they may no longer be backed by real collateral. This is why checking a bridge’s security track record matters just as much before you bridge as while you’re bridging.
How do I know if my bridge transaction is stuck or failed?
Check the transaction hash on a block explorer for both the source and destination chains, like Etherscan or Solscan. Most bridges also have a status tracker on their own site where you can paste your transaction hash. If it’s been well beyond the bridge’s normal settlement time with no update, contact the bridge’s support channel with your transaction details.
Can bridge transactions be reversed if I sent them to the wrong address?
No, blockchain transactions, including bridge transfers, are generally final once confirmed. Double-check the destination address and the destination chain carefully before confirming any bridge transaction, since there’s usually no way to undo it.
Disclaimer: This article is intended solely for informational purposes and should not be considered trading or investment advice. Nothing herein should be construed as financial, legal, or tax advice. Trading or investing in cryptocurrencies carries a considerable risk of financial loss. Always conduct due diligence before making any trading or investment decisions.
Trade with proof of Reserves
UEEx publish monthly audits and third party verification on every listed market.